
Unlock Robust API Security with Expert Testing

What is API Pentesting?
Why Do You Need?
Proactive Vulnerability Identification
Compliance with Data Protection Standards
Securing Sensitive Data Transfers
Building Trust in Digital Services
Tailored Approaches for
Advanced API Security
Customized Vulnerability Assessments
API Contract Review
Authentication and Authorization Checks
Business Logic Testing
Data Encryption and Transmission Security Assessments
Remediation and Security Enhancement Guidance
Enhance Your API Security Today
Our API Penetration Testing Methodology
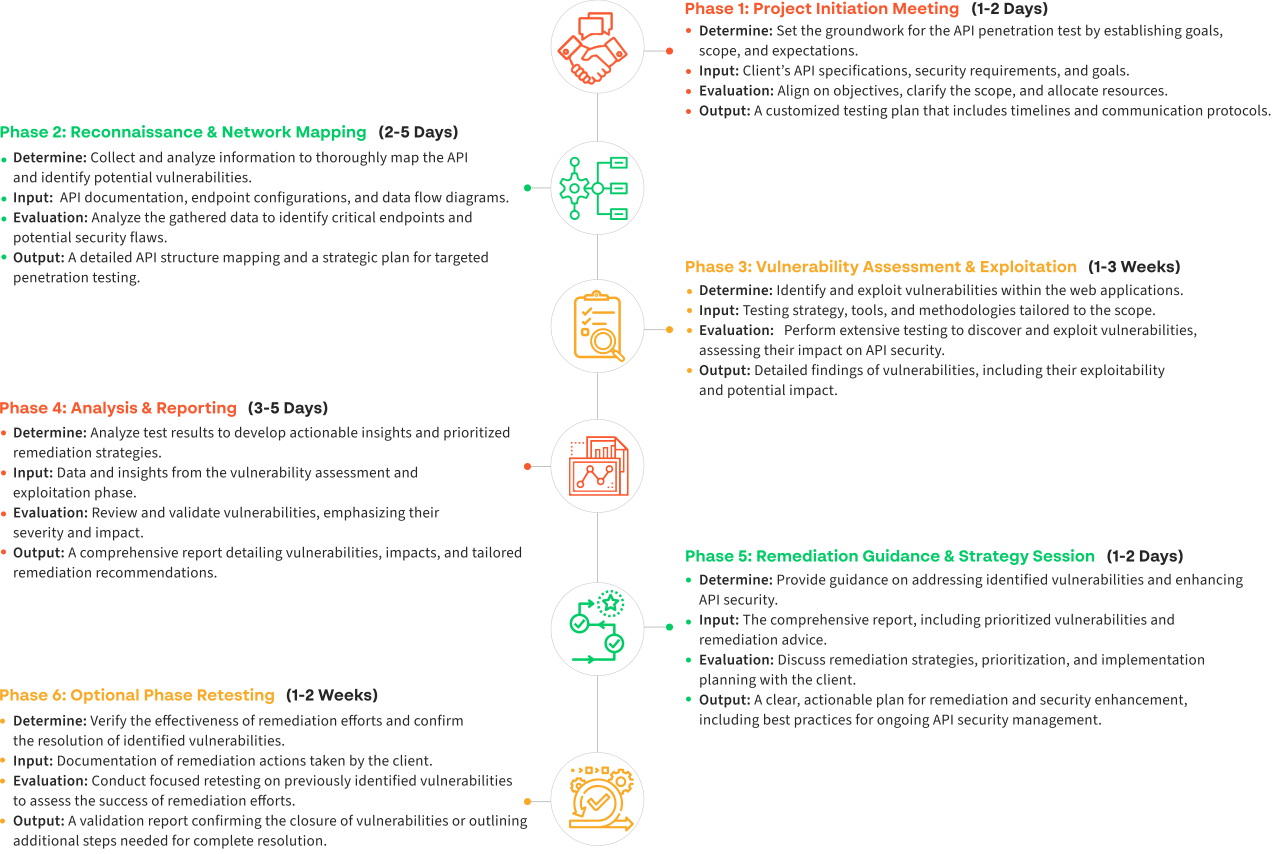
Initial Consultation & Scope Definition
We begin by understanding your specific requirements and the scope of your APIs, setting a tailored strategy that aligns with your organization's needs. This initial step establishes the groundwork for a focused and effective penetration test.
Reconnaissance & API Mapping
During this phase, we perform extensive data gathering to map out your API landscape. We identify all endpoints, associated methods, and data handling practices. This comprehensive mapping helps in pinpointing potential vulnerabilities and planning precise test scenarios.
Vulnerability Assessment
Using a combination of advanced automated tools and detailed manual testing, we systematically assess your APIs for vulnerabilities. This includes checks for security flaws in authentication, authorization, input validation, and overall API business logic, ensuring thorough coverage and alignment with top security standards.
Exploitation & Impact Analysis
We simulate controlled attacks to validate identified vulnerabilities, determining their exploitability and the potential impact on your API's security. This critical phase highlights real-world attack vectors and the possible consequences of security weaknesses.
Reporting & Strategic Remediation
Our detailed reporting concludes the testing phase, providing a clear and actionable overview of all identified vulnerabilities, their severity, and prioritized remediation strategies. This report is designed to guide your security team through the remediation process, enhancing your API's defenses and ensuring continued protection.
API Security Timeline:
Precision and Protection Throughout

Frequently Asked Questions
- Annually, as a regular security measure.
- Whenever significant changes are made to the API, such as updates or the introduction of new features.
- After deploying any security patches to ensure they are effective and do not introduce new vulnerabilities.
- A summary of the vulnerabilities discovered.
- An assessment of their potential impact.
- Prioritized recommendations for remediation, tailored to your specific API environment.
Full-Spectrum
Penetration Testing Services
Web App Test
Network Test
Cloud Security Audit


