
Next-Level Security for Your Web Applications

What is Web App Pentesting?
Why Do You Need?
Identify Hidden Vulnerabilities
Compliance and Regulatory Assurance
Enhanced Customer Trust
Stay Ahead of Cyber Threats
AI Aegis Lab’s Web App
Penetration Testing Services
Custom Vulnerability Assessments
OWASP Top 10 & SANS Top 25 Alignment
Automated and Manual Testing Techniques
Remediation Strategies and Support
Continuous Monitoring and Reassessment
Comprehensive Compliance Reporting
Start Your Journey to Secure Web Applications
Web App Penetration Testing Methodology
Initial Consultation & Scope Definition
We initiate our process by understanding your unique requirements, objectives, and the breadth of your web environment, setting the stage for a customized testing strategy.
Reconnaissance & Threat Modeling
This phase involves gathering information on your web applications to identify potential vulnerabilities and threat vectors, combining detailed reconnaissance with threat modeling to prioritize risks and tailor our approach.
Vulnerability Assessment
Through a mix of automated scanning and meticulous manual testing, we pinpoint vulnerabilities by benchmarking against databases like CVEs and adhering to standards such as OWASP Top 10 and SANS Top 25.
Exploitation & Validation
Simulating real-world attacks, we validate the vulnerabilities' exploitability to understand their potential impact, demonstrating how attackers could leverage them in a controlled manner to compromise your web applications.
Reporting & Remediation Guidance
Our final report delivers a comprehensive analysis of our findings, including vulnerability details, their criticality, and practical steps for remediation. We provide tailored advice to fortify your web applications against future threats.
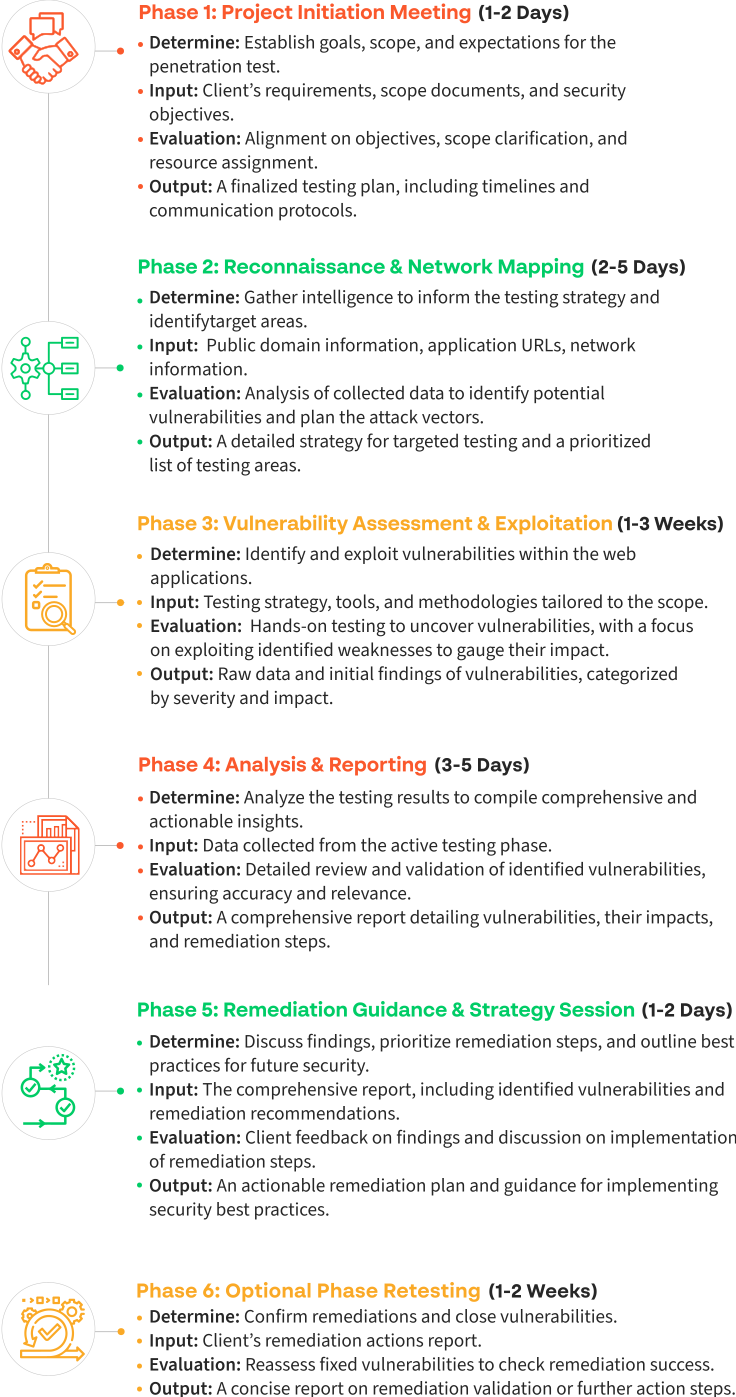
Web App Security Timeline:
From Start to Secure

Frequently Asked Questions
- Significant changes are made to the application or its environment.
- New features are added.
- Security patches are applied.
- Regulatory requirements mandate testing.
- A summary of the vulnerabilities discovered.
- An assessment of their impact.
- Prioritized recommendations for remediation. The report is designed to provide actionable insights to improve your web application’s security posture.
Full-Spectrum
Penetration Testing Services
Network Test
API Pentest
Cloud Security Audit


